Connect with us
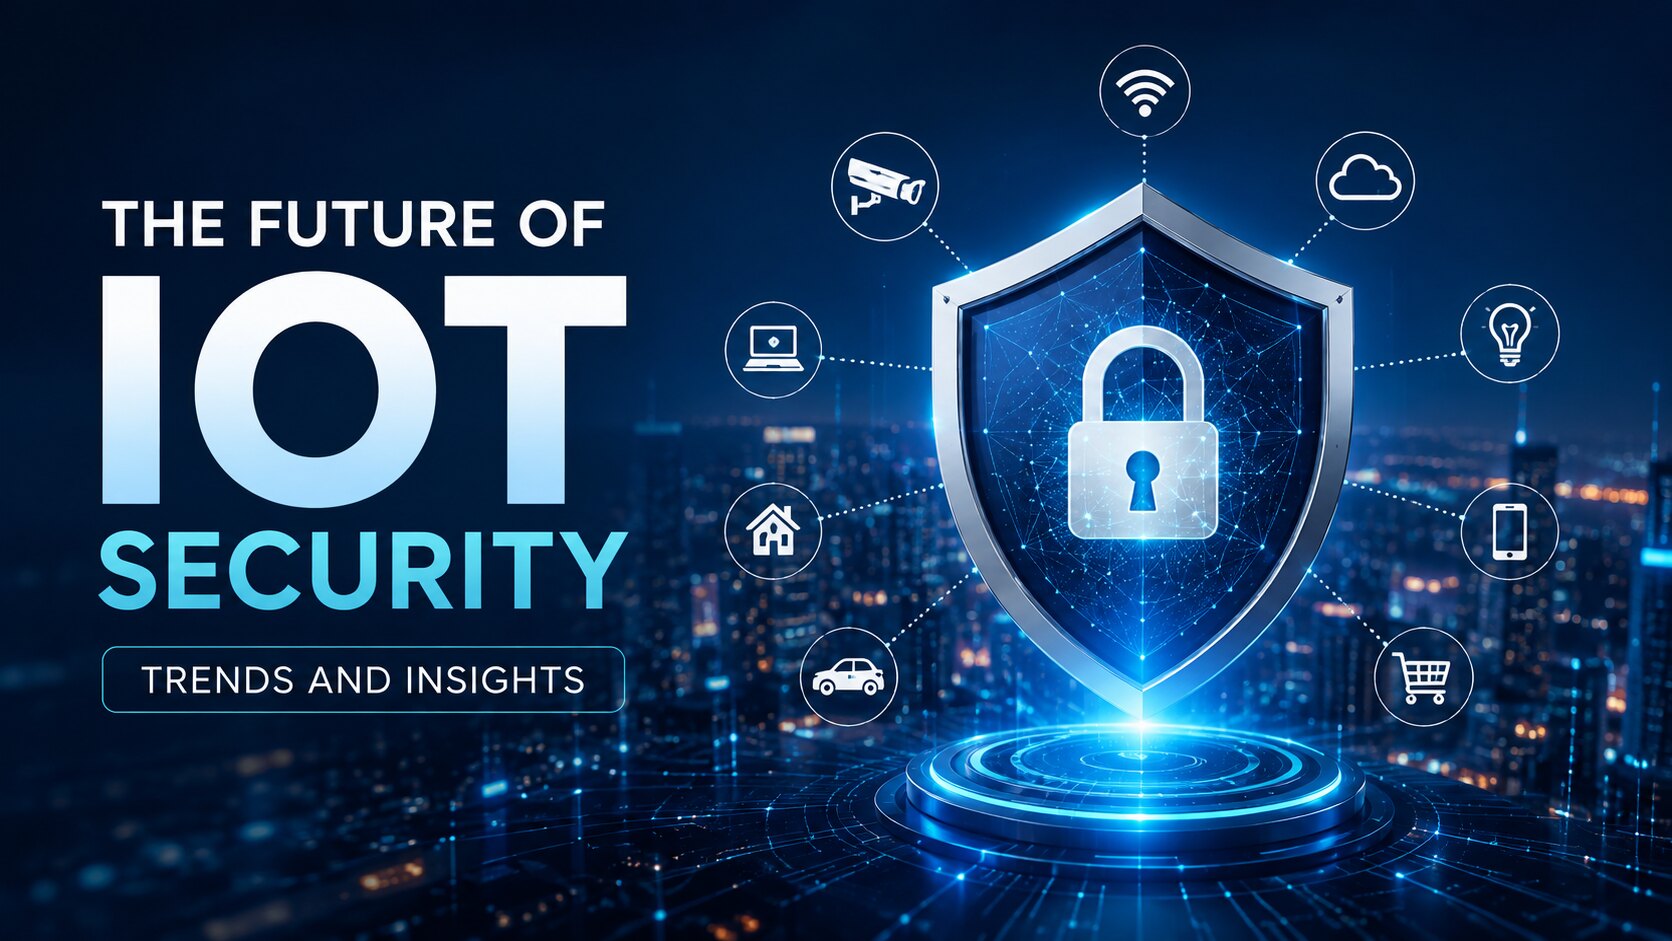
The Future of IoT Security: Trends and Insights
IoT security is the practice of protecting internet-connected devices, networks, and data from cyber threats and unauthorized access. As connected technology becomes more common across homes, businesses, and industries, securing these systems is essential to prevent vulnerabilities and protect sensitive information.
This blog explores the reasons behind the growing need for IoT security, the main types of security controls, emerging trends, and practical ways organizations can strengthen protection for their connected devices.
Reasons for the growing attention to security protocols
The growing number of connected devices has expanded the potential attack surface for cybercriminals. Smart home devices, industrial sensors, connected healthcare equipment, and business systems can all become entry points if they are not properly secured. A compromised device may expose sensitive data, disrupt operations, or provide access to other systems on the same network.
Organizations are paying greater attention to IoT security for several reasons:
- Vulnerability management: Identify and fix weaknesses in device hardware, software, and network configurations.
- Data encryption: Protect information while it is transmitted between devices and services and, where appropriate, while it is stored.
- Identity and access management: Ensure that only authorized users and devices can access sensitive systems.
- Network segmentation: Separate IoT devices from critical business systems to limit the impact of a compromised device.
- Continuous monitoring: Detect unusual device activity and potential threats before they spread.
The right combination of security controls depends on the device, the data it handles, the environment in which it operates, and the level of risk involved.
Why should you care about security?
IoT security matters because connected devices collect, process, and exchange information that may be sensitive or essential to daily operations. Weak security can expose personal data, interrupt services, and allow attackers to move from a vulnerable device into other connected systems.
The main reasons to prioritize IoT device security include:
- Privacy protection: Secure personal, customer, and business information from unauthorized access.
- Operational reliability: Reduce the risk of device failures, service interruptions, and disruptions caused by cyberattacks.
- Financial risk reduction: Limit potential costs associated with data breaches, system recovery, and operational downtime.
- Customer and business trust: Demonstrate that connected products and services are designed and managed with security in mind.
- Growing device adoption: Apply appropriate safeguards as organizations connect more devices across offices, facilities, and remote locations.
IoT security should be considered throughout a device's lifecycle, from initial setup and deployment to maintenance, software updates, and eventual retirement.
How IoT Devices Create Security Risks
IoT systems typically combine physical devices, sensors, software, network connections, and services that collect or exchange data. These components create several points that attackers may target.
- Device vulnerabilities: Outdated firmware, insecure default passwords, or weak device configurations can expose connected equipment.
- Communication risks: Poorly protected connections may allow attackers to intercept or manipulate data.
- Application vulnerabilities: Weak authentication, excessive permissions, and insecure software can expose device functions or user information.
- Cloud and platform risks: Misconfigured storage, compromised accounts, or inadequate access controls can put remotely stored data at risk.
Understanding these risks helps organizations select suitable IoT security controls for their devices, applications, networks, and cloud environments.
Key Types of IoT Security
Effective IoT security requires protection across devices, communication channels, applications, and data storage. The following security layers help organizations reduce vulnerabilities and manage access to connected systems.
Network Security
IoT network security protects connected devices and the networks through which they communicate. Network segmentation, firewalls, secure communication protocols, and continuous traffic monitoring can help restrict unauthorized access and identify suspicious activity. Separating IoT devices from critical business systems can also limit the damage if a device is compromised.
Application and Device Security
Application and device security focuses on protecting device software, firmware, interfaces, and applications. Secure development practices, strong authentication, least-privilege permissions, and timely security updates help address common vulnerabilities. Organizations should also replace default credentials and ensure devices can receive security patches throughout their supported lifecycle.
Cloud Security for IoT
Many IoT systems send data to cloud platforms for storage, analysis, and remote management. Cloud security controls include encryption, multi-factor authentication, role-based access, secure configuration, and activity logging. Regularly reviewing permissions and monitoring account activity can help detect suspicious access and reduce the risk of data exposure.
These security layers work best when they are implemented together as part of a broader IoT security strategy.
What Are the Future Trends in IoT Security?
The future of IoT security will be shaped by the growing number of connected devices, increasingly sophisticated cyber threats, and the need to protect data across complex systems. Organizations will need to move beyond basic security controls and adopt practices that support continuous monitoring, faster response, and long-term device protection.
AI-Assisted Threat Detection
Security teams can use artificial intelligence and machine learning to analyze device activity, identify unusual patterns, and prioritize potential threats. These tools can help accelerate detection, although their results still require appropriate validation and oversight.
Zero-Trust Access Controls
Zero-trust security follows the principle of verifying every user, device, and access request rather than automatically trusting devices inside a network. Strong authentication, least-privilege permissions, and continuous verification can help limit unauthorized access.
Stronger Device Identity and Authentication
As IoT networks grow, organizations need reliable ways to identify devices and verify that they are legitimate. Unique device identities, secure credentials, and appropriate authentication methods can reduce the risk of unauthorized devices connecting to critical systems.
Secure Firmware Updates and Device Lifecycles
Devices need a reliable way to receive authenticated software and firmware updates. Manufacturers and organizations must also plan for vulnerability fixes, ongoing support, and the secure retirement of devices that are no longer maintained.
Greater Focus on Data Privacy and Encryption
Encryption and careful data-handling practices will remain important as connected devices collect and transmit sensitive information. Organizations should limit data collection to legitimate needs, control who can access it, and protect it during transmission and storage.
These IoT security trends are not standalone solutions. Organizations should combine suitable technologies with clear security policies, regular risk assessments, staff training, and incident response plans to protect connected systems as threats evolve.
How to Improve IoT Security
Organizations can strengthen IoT security by applying practical safeguards throughout the device lifecycle.
- Change default credentials: Use strong, unique passwords and enable multi-factor authentication where supported.
- Keep devices updated: Apply verified firmware and software updates to address known vulnerabilities.
- Secure network connections: Use appropriate encryption, firewalls, network segmentation, and secure communication protocols.
- Restrict access: Give users and devices only the permissions they need to perform their tasks.
- Monitor device activity: Review logs and network traffic for unusual behavior, unauthorized access, or unexpected data transfers.
- Assess suppliers and devices: Review manufacturers' security practices, update policies, and support commitments before deployment.
- Prepare for incidents: Establish a response plan for isolating compromised devices, investigating threats, restoring services, and notifying affected parties when required.
- Train employees: Help staff recognize security risks, follow device-management procedures, and report suspicious activity.
No single measure can eliminate every IoT security risk. A layered approach that combines technical controls, monitoring, maintenance, and clear responsibilities provides more reliable protection than relying on one security tool alone.
Conclusion
Securing the Internet of Things requires more than choosing a security tool or hiring trained specialists. It involves identifying vulnerabilities, protecting device communications, managing access permissions, securing cloud environments, and keeping software up to date. As IoT adoption grows, emerging approaches such as AI-assisted threat detection and zero-trust access controls can help organizations respond to evolving security risks.
Ultimately, effective IoT security depends on combining the right technologies with continuous monitoring, regular updates, and clear security practices. Organizations that make security part of the entire device lifecycle will be better prepared to protect sensitive data, maintain reliable operations, and manage the risks associated with an increasingly connected world.
FAQ's
1. What is IoT security?
IoT security refers to the technologies, strategies, and best practices used to protect internet-connected devices, the networks they operate on, and the data they generate from cyber threats. It covers network security, application security, and cloud security, since IoT devices constantly collect and transmit personal or business information. As more devices connect to the internet, from home gadgets to industrial sensors, strong IoT security becomes essential to prevent unauthorized access, data leaks, and hacker attacks that could compromise users and companies alike.
2. Why is IoT security important?
IoT security is important because connected devices constantly collect and share personal data, making them attractive targets for fraudsters and cybercriminals. Without proper protection, sensitive information can fall into the wrong hands, leading to privacy violations, financial loss, or reputational damage for companies. As reliance on IoT grows across homes and businesses, strong security builds customer trust, protects supplier interests, and ensures the long-term value of connected technology isn't undermined by preventable data breaches or unauthorized access.
3. What are the main types of IoT security?
The main types of IoT security are network security, application security, and cloud security. Network security prevents unauthorized users from accessing the systems where data is stored. Application security controls what data apps can collect and blocks unpermitted tracking or automatic transfers. Cloud security protects information stored remotely, monitoring third-party access and system changes. Together, these layers address different points where IoT data can be exposed, giving companies a more complete defense against evolving cyber threats.
4. What makes a product an IoT system?
A product qualifies as an IoT system if it demonstrates measuring, identification, interconnection, and recommendation capabilities. Measuring refers to using virtual computing tools to collect data. Identification assigns a unique identifier to devices and owners. Interconnection allows the device to monitor and transfer data to other systems, with user permission. Recommendations come from analyzing collected data to generate real-time insights or solutions. These combined features distinguish true IoT products from standard connected applications.
5. What does the future of IoT security look like?
The future of IoT security involves growing investment as cybercriminals develop new ways to bypass existing protections. Companies will need faster threat detection, stronger encryption, and more adaptive protocols to keep pace. Success will depend on understanding audience needs, implementing modern security measures, and clearly communicating improvements to users. While demand for IoT continues rising, security providers must treat protection as an ongoing, evolving process rather than a one-time fix to maintain trust and reduce risk.