Connect with us
The Offboarding Test: Can Your Messaging Workflow Survive When Someone Leaves?
Most communication problems stay hidden while the right people are still around. A project manager knows where the final contract lives. A contractor remembers which client group is still active. Someone on the sales team knows why a supplier was moved to a different thread. None of it feels fragile, because the people carrying the context are still one message away.
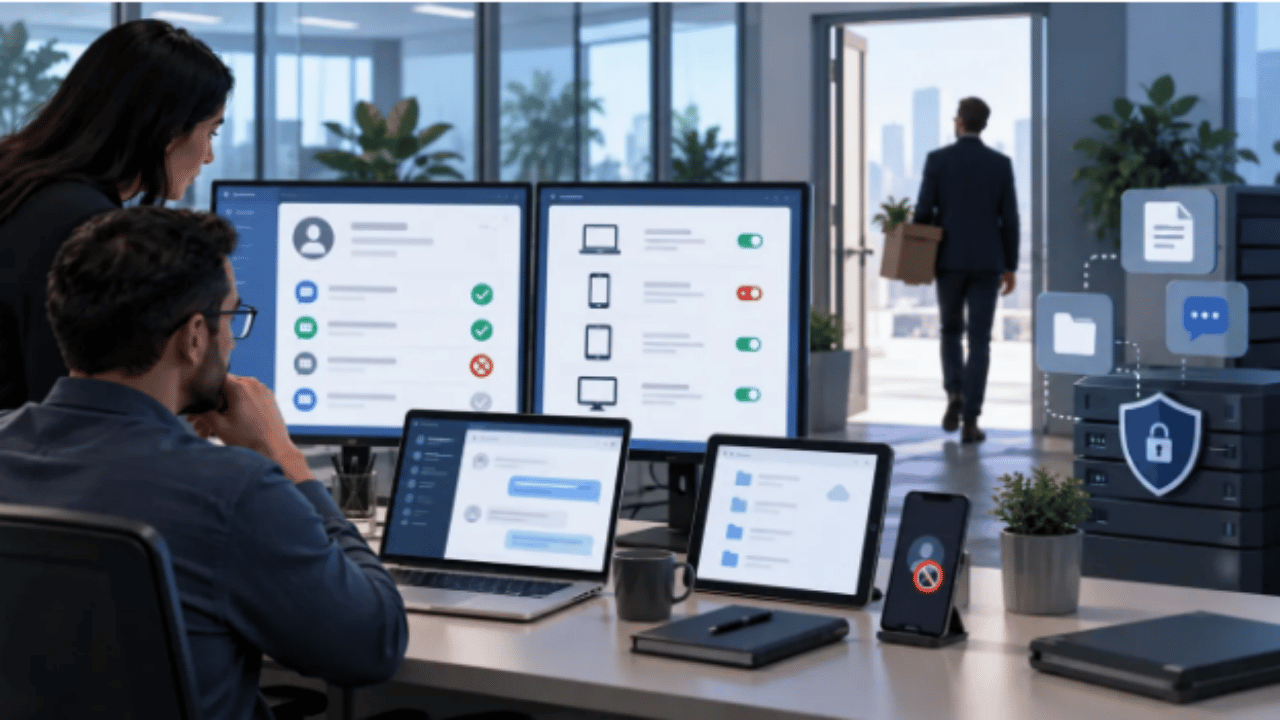
Then one of them leaves. On Monday morning the team discovers that a client conversation was started from a personal account, a key file exists only as a chat attachment, an old laptop may still be signed in, and the incoming project lead cannot tell which decision was final. A team communication platform can help centralize conversations, files, and access, but only when ownership and offboarding processes are clearly defined.
That looks like an offboarding failure, and it is. But it is also a communication-design failure. A messaging workflow is only as resilient as the ownership, access and recordkeeping sitting behind it. This guide walks through the pressure points a departure exposes accounts, group admin rights, files, decisions, contractors and device sessions and gives you a simple exercise for finding them before anyone resigns.
Start With the Account, Not the Chat
Before asking who manages a group, ask who controls the identity that joined it.
A personal messaging account may be tied to an employee’s own phone number, device and recovery methods. The company can rely on that account every day without actually controlling it. That distinction is easy to ignore until the employee changes roles, loses a device or leaves the business.
Company-managed identities work differently. They can be provisioned, restricted and revoked through organizational controls rather than depending on the individual user to clean up access.
For teams with Chinese-speaking staff, resources such as an Telegram Account Usage Guide can help employees understand the personal-account side of settings and access. For the organization, however, the more important question is whether business communication can be withdrawn from a departing user without depending on that person to cooperate.
That is the first offboarding test.
Removing Someone From a Group Is Only One Step
A team can remove a departing employee from a channel and still leave several access problems unresolved.
The practical questions are more specific:
- Is the employee still signed in on a work laptop, home computer or browser?
- Are they the only administrator of an important external group?
- Do customers or vendors know only their personal messaging identity?
- Are shared files stored anywhere outside the conversation?
- Can the company retrieve important decisions after the person leaves?
- Do any bots, integrations or shared credentials still depend on them?
If the answer is “we need to ask the employee,” the workflow has an operational dependency on that person.
Offboarding works best when these questions have answers before anyone resigns.
Group Admin Rights Do Not Equal Enterprise Control
Adding a second group administrator is useful. It removes one obvious single point of failure.
It does not solve identity lifecycle, retention, auditing or device policy.
A group administrator may be able to add or remove members and change group permissions. Enterprise administration is concerned with a wider set of controls: who can be provisioned, which roles can access which spaces, how records are retained, whether access can be revoked centrally and whether administrators can review activity later.
That difference matters most as an organization grows. A ten-person team can operate for years on social habits and institutional memory. A hundred-person business eventually needs controls that survive staff turnover.
This is where enterprise collaboration platforms begin to differ materially from consumer messaging tools. The issue is not whether a consumer app is secure enough for a private conversation. The issue is whether the organization can administer the communication environment as an organizational asset.
Files Are Usually Where Weak Ownership Shows Up First
Chat makes file sharing effortless. That convenience can hide a version-control problem.
Imagine seeing Final Contract.pdf in a project conversation. Is it actually the final contract? Was a revised copy sent two days later? Is the signed version in the company drive? Does the replacement account manager know where the authoritative copy sits?
The answer should not require scrolling through months of messages.
Messaging is a good place to discuss a file. It is a poor place to make ownership of that file ambiguous. Contracts, approved creative assets, customer records and final project documents should live in a repository the organization controls.
The chat can preserve the conversation around the document. The document system should preserve the document.
Decisions Need Somewhere to Land
The same problem applies to approvals and decisions.
“Approved in chat” may be perfectly adequate for a quick operational choice. It becomes fragile when the decision affects a contract, customer commitment, budget or regulated process and the only evidence is buried in a conversation.
Teams do not need to copy every chat message into another system. They do need a rule for the moments that change business state.
A useful pattern is simple: discuss in chat, record the outcome where the work is managed.
That might mean updating a CRM record, moving a ticket, changing a project status, attaching the approved file to a shared workspace or noting the final decision in a meeting record.
The goal is not more documentation. It is less dependence on memory.
Contractors Expose the Weak Spots Faster
External contractors are often where communication governance becomes messy.
A full-time employee may have a company email address, managed laptop and directory account. A contractor may join from a personal phone, use an external email address and communicate through an account the business does not own.
That is not automatically a problem. It becomes one when no one has decided what that access is allowed to carry.
Before a contractor joins a project, decide where final files will live, which conversations may contain customer information, who owns the project groups and what should happen on the contractor’s last day.
If offboarding requires reconstructing those rules after the contract ends, the controls arrived too late.
Device Sessions Deserve Their Own Check
Account ownership is only part of access. Authorized devices are another.
A single messaging identity may be active on a phone, browser, home computer and work laptop at the same time. When a device changes hands or an employee leaves, those sessions matter.
Telegram, for example, lets users review and terminate active device sessions. For people who need a practical refresher on how those logins work across phones, browsers and computers, a Telegram login and session guide can clarify the user-controlled side of device access.
Enterprise offboarding goes further. IT should not have to depend on a departing employee remembering every signed-in device and voluntarily closing each session. Where business risk requires centralized revocation, the communication platform and identity system need controls designed for that job.
Personal Security Is Not the Same as Organizational Governance
The distinction is easy to miss because the same words access, security and authentication appear in both conversations.
A user can protect a personal messaging account with stronger authentication, device reviews and local passcodes. Those measures reduce risk to the individual account.
The company is solving a different problem.
It needs to know whether access can be revoked after a role change, whether records remain available, whether administrators can investigate an incident, whether external sharing can be limited and whether company data remains under company control.
A well-secured personal account can still be a poor place for a controlled business process.
That does not make consumer messaging tools useless at work. It means their role should be deliberate.
Draw a Boundary Around What Belongs in Consumer Messaging
Many organizations already operate with more than one communication layer. Trying to force every conversation into one system can be as impractical as letting every team choose its own unmanaged tool.
A workable policy can be based on risk rather than brand names.
Informal communities, networking groups and low-risk external coordination may be fine in consumer messaging. Day-to-day operational discussion may require clearer rules around files, ownership and response expectations. Sensitive customer data, formal approvals, legal records and regulated information belong in systems the organization can administer and retain appropriately.
The important part is that employees should not have to guess which category a conversation belongs to.
If the policy only exists in the security team’s head, it is not a usable policy.
Run the “They Leave Tomorrow” Exercise
A fast way to find weak points is to choose a real role and pretend that person leaves tomorrow with no time for a handover.
Can the team answer these questions in a few minutes?
Identity: Who owns the account used for work conversations?
Access: Who can revoke it?
Devices: Can active endpoints be identified and removed?
Groups: Is there another administrator for important spaces?
Files: Are final documents in company-controlled storage?
History: Can a replacement employee recover key decisions without asking former staff?
External relationships: Do customers and suppliers have a durable company contact?
Integrations: Are bots, automations and connected services documented?
This exercise is more useful than a generic security checklist because it tests the workflow under the exact condition most likely to expose hidden ownership.
Know When You Have Outgrown Informal Messaging
Small teams can work effectively with lightweight tools for a long time. The tipping point is usually not headcount by itself.
It is the moment when the business starts needing capabilities such as centralized provisioning, role-based permissions, audit history, retention rules, managed external access, SSO, organization-controlled deprovisioning or deployment requirements that a personal messaging service was never designed to handle.
At that point, communication is no longer only about sending messages quickly. It becomes part of the company’s identity, security and records architecture.
This is the territory enterprise collaboration products are designed for. Consumer messaging can continue to serve communities or low-risk external conversations, but the system holding controlled business communication should match the level of governance the business actually needs.
The Best Offboarding Process Starts Before Anyone Leaves
A clean exit is rarely the result of a heroic final-day checklist.
It comes from ordinary decisions made months earlier: company-owned identities where they are required, more than one administrator for critical groups, files stored outside personal chat history, important decisions recorded in the right system and clear rules for external collaborators.
If those foundations are in place, offboarding becomes routine.
If they are not, an employee departure turns into a search for missing context, forgotten sessions and undocumented ownership.
That makes offboarding a useful stress test for any communication stack.
Frequently Asked Questions
1. What is an offboarding test for a messaging workflow?
An offboarding test is a simple exercise: pick a real role, assume that person leaves tomorrow with no handover, and see whether the team can still answer basic questions about identity, access, devices, files and decisions. It is more revealing than a generic security checklist because it stresses the workflow under the exact condition most likely to expose hidden ownership and undocumented dependencies. Run it quarterly, not after a resignation.
2. Why is removing someone from a group not enough?
Removing a departing employee from a channel closes one door and leaves several open. They may still be signed in on a home computer or browser, remain the sole administrator of an important external group, or be the only contact your customers recognise. Shared files, bots and connected services can also depend on them. If answering those questions requires asking the employee, the workflow still depends on them.
3. What is the difference between group admin rights and enterprise control?
A group administrator can usually add or remove members and change group permissions, which removes one obvious single point of failure. Enterprise administration covers a wider set of controls: who can be provisioned, which roles reach which spaces, how records are retained, whether access can be revoked centrally, and whether administrators can review activity afterwards. Adding a second admin helps, but it does not deliver identity lifecycle or retention.
4. Where should final files and decisions actually live?
Chat is a good place to discuss a document and a poor place to own it. Contracts, signed agreements, approved creative assets and customer records belong in a repository the organisation controls, so a replacement never has to scroll months of messages to find the authoritative copy. Decisions that change business state should land where the work is managed: a CRM record, a ticket, a project status.
5. When has a company outgrown informal messaging tools?
The tipping point is rarely headcount alone. It arrives when the business needs centralised provisioning, role-based permissions, audit history, retention rules, managed external access, single sign-on or organisation-controlled deprovisioning. At that stage communication is no longer just about sending messages quickly; it forms part of your identity, security and records architecture. Consumer tools can still serve communities and low-risk external contact, provided that role is deliberate.