Connect with us
How Development Teams Can Collaborate on MISRA Compliance
MISRA efforts can stall when one engineer owns the checker, everyone else treats its output as background noise, and the compliance report is assembled just before an audit. The problem isn't necessarily the rules. It's the lack of shared responsibility.
MISRA Compliance:2020 treats compliance as an ongoing development process, not a final check. Its planning documents, enforcement records, and deviation records give teams a common way to describe what they check, how they check it, and who reviews the results.
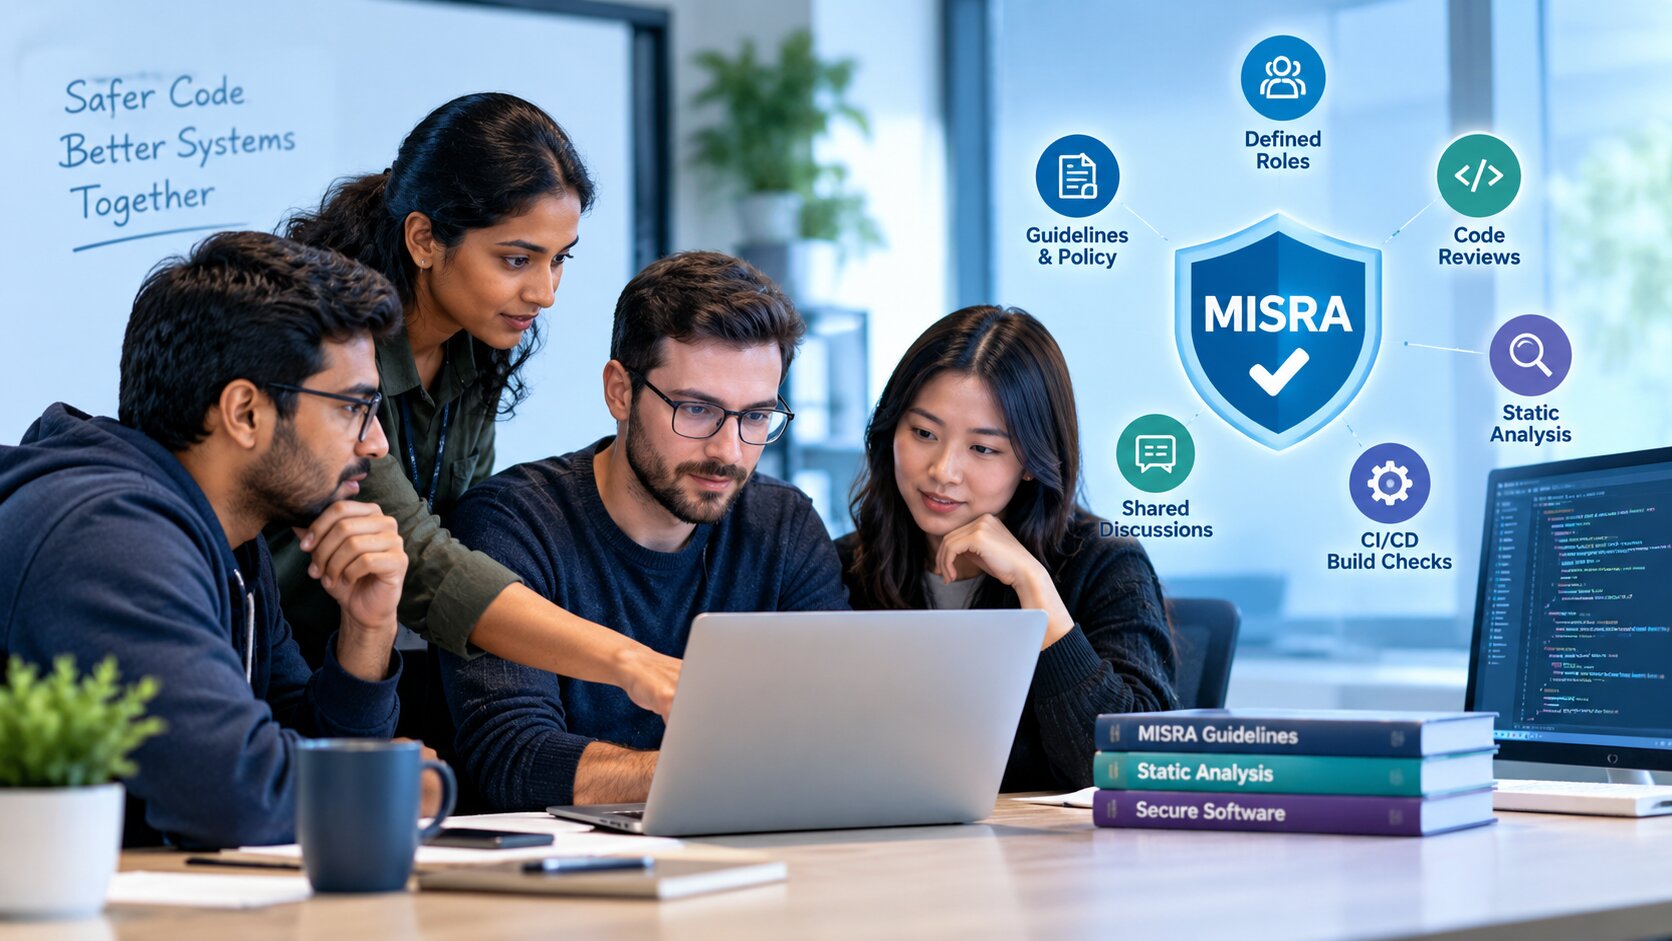
A workable process connects those documents to everyday engineering: clear ownership, static analysis that examines code without running it, code review, and build checks. It also distinguishes progress toward compliance from a completed compliance claim.
Key Takeaways
- Policy comes before tooling. Agree on the Guideline Re-categorization Plan (GRP) and Guideline Enforcement Plan (GEP) early so findings have a clear meaning.
- Tools need human review. Analysis coverage and false positives vary. Record where reviews or other verification methods are needed.
- Gate new code and plan legacy fixes. Preventing new violations helps control the backlog, but unresolved legacy violations still affect compliance.
- Deviations need justification. Mandatory guidelines cannot be deviated from. Other departures must follow the applicable compliance process.
- Static analysis complements testing. A clean report does not establish functional correctness or provide safety certification.
Which MISRA Are We Talking About?
Before agreeing on policy, agree on the target edition. A C project may be working to MISRA C:2023, MISRA C:2025, or an earlier contractual baseline. For C++ projects, MISRA C++:2023 targets C++17. Record the chosen edition and any applicable amendments or corrections rather than simply specifying “MISRA compliance.”
Security requirements also need attention. MISRA publishes mappings to other guidance, including ISO/IEC TS 17961 for C security. These mappings can help teams reuse evidence, but they do not replace an assessment of the product's security requirements.
The chosen edition determines the guideline identifiers in the GRP and GEP, the analyzer profile, and the language configuration. A profile for one edition should not be assumed to cover another. Check that the compiler settings, analyzer settings, and project documents describe the same target.
Roles and Operating Model
You don't need a large committee. You need clearly owned responsibilities. A lean model can include:
- MISRA lead: owns the GRP and GEP, coordinates deviation reviews, and handles compliance questions.
- Tool champion: maintains analyzer configuration, guideline mappings, tool versions, and false-positive investigations.
- Reviewers: handle checks that analysis cannot fully perform and record their conclusions.
- Safety or quality lead: reviews the impact of deviations and confirms that evidence is retained.
- Continuous integration (CI) owner: maintains build checks, merge gates, and report storage.
One person may hold several roles, but ownership should remain explicit. Record names in the project plan and update them when responsibilities change. Include training on the selected guidelines, tool limitations, and the process for reviewing findings so compliance doesn't depend on one specialist. Keep triage decisions and review discussions in shared, searchable spaces; the right collaboration tools make past rulings easy to find when the same finding comes up again.
Start With Policy: The Guideline Re-categorization Plan (GRP)
The GRP records how the project treats each guideline's category. MISRA Compliance:2020 calls for agreement between the acquirer and supplier at project start. It allows categories to be strengthened and Advisory guidelines to be designated Disapplied. Mandatory guidelines remain Mandatory; Required guidelines cannot simply be downgraded to avoid findings.
The illustrative entries below use MISRA C:2023 identifiers. Each rationale explains a project decision, not a recommendation that every team should adopt.
| Guideline | MISRA category | Project category | Rationale |
| Rule 12.4 | Advisory | Required | Prevent unsigned wraparound in constant expressions used for timer calculations. |
| Rule 15.5 | Advisory | Disapplied | Allow guard clauses, with exit paths assessed during code review. |
| Rule 8.13 | Advisory | Advisory | Report findings and review them without automatically blocking merges. |
| Rule 9.1 | Mandatory | Mandatory | The category cannot be lowered and deviations are not permitted. |
Distinguish code developed by the team from adopted third-party code and generated code. Document the applicable treatment and its justification rather than assuming every component has the same obligations or evidence.
Decide how shared headers are handled, too. A finding in a header can appear in many separately compiled source files. Record its scope clearly so repeated diagnostics don't become inconsistent decisions or duplicate deviation records.
Make Enforcement Explicit: The Guideline Enforcement Plan (GEP)
The GRP sets the project categories. The GEP explains how each guideline is checked. A practical GEP can use one row per rule or directive, recording the guideline, project category, analyzer check, relevant configuration, manual review needs, and supporting evidence.
For example, an entry for Rule 17.7 can identify the analyzer check for discarded return values of non-void functions, describe its coverage, and state how any gaps are reviewed. Use the vendor's actual guideline mapping rather than assuming a similarly named check provides complete coverage.
Some guidelines are classified as undecidable: no analysis method can determine compliance for every possible program. Rule 1.3, concerning undefined behavior, illustrates why a tool's coverage must be understood. The GEP should identify what analysis checks and what additional review or verification is needed.
MISRA Compliance:2020 recognizes that tools cannot guarantee detection of every violation without false positives. If the team uses a fast configuration for pull requests and a deeper configuration overnight, document the difference and when the full results must be resolved.
Record the compiler, analyzer, rule pack, and relevant settings used for each release. When the toolchain changes, review the GEP and rerun affected checks. Retain earlier evidence with its original configuration rather than treating reports from different versions as interchangeable.
Baseline and Triage at Scale
The first scan of an established codebase can produce a large backlog. A baseline helps separate existing findings from newly introduced ones so the team can improve the code without losing track of unresolved work.
Run analysis on the main branch and retain the results. Then prevent new Mandatory violations and new Required violations without approved deviations. Triage existing findings by safety and security impact, guideline category, and affected functionality. Mandatory violations must be resolved before a compliance claim; they cannot be accepted through deviation.
Triage works well in pairs: the tool champion explains the diagnostic, and the module owner assesses the code. Record whether the finding is a confirmed violation, a false positive supported by evidence, or a potential deviation requiring review. A suppression alone does not settle that decision.
Keep the GRP, GEP, deviation records, guideline compliance summary, and build records together. The summary should show guideline status and relevant deviation references. Build records should identify the sources, configuration, and tools behind the results.
A clean-new-code gate is a development control, not proof that the whole codebase complies. Keep the legacy backlog visible and assign owners and resolution dates.
CI/CD Guardrails for MISRA
A continuous integration and delivery pipeline can make checks repeatable and keep evidence tied to the code being released:
- Capture the build configuration. Give the analyzer the production build's flags, definitions, and include paths through a compilation database or supported build integration.
- Analyze pull requests. Run suitable checks on changed code and show findings where developers review the change. Account for changes that affect other files.
- Apply the quality gate. Block unresolved new Mandatory findings. Block new Required findings unless an applicable deviation has been approved. Use the GRP's project categories.
- Run full-project analysis. Schedule broader checks for dependencies across source files and analyses too slow for routine pull requests. Define how failures are assigned and resolved.
- Publish evidence. Store reports and build records with the release artifacts so the evidence can be traced to the delivered version.
Several tools support parts of this workflow. SonarQube provides MISRA-related C/C++ checks, while Klocwork offers MISRA-oriented reporting. Verify support for the exact edition, language, and reporting needs in your GEP rather than choosing by a general compliance label.
Parasoft's MISRA solution combines static analysis, IDE and CI/CD integration, and compliance reporting. These capabilities can help teams connect findings and compliance evidence to development work instead of maintaining a separate reporting process.
Whatever tooling you choose, generate evidence from checks on the release sources and build configuration. Do not assume a partial pull-request scan provides the same coverage as full-project analysis.
Apply gates consistently with the GRP. Advisory guidelines raised to Required should be treated as Required. Guidelines that remain Advisory can be tracked and reviewed without automatically blocking every merge.
Deviations Without Chaos
A deviation is a documented, justified departure from a guideline where deviations are permitted. MISRA Compliance:2020 distinguishes a deviation record for a specific departure from a deviation permit that provides a reusable basis under stated conditions. A permit does not remove the need to establish that those conditions apply.
For example, a hardware abstraction layer may need integer-to-pointer conversions for register access, which Rule 11.4 addresses. Rule 11.4 is Advisory by default; if the GRP raises it to Required, agreeing on a suitable permit can reduce repeated reasoning, but each use still needs the required assessment and traceability. Mandatory guidelines are not eligible for deviation.
Keep source annotations short and link them to the full record. An illustrative tag such as /* MISRA-DEV: DEV-0042 */ can provide traceability, but it will not necessarily suppress a diagnostic. Use the analyzer's supported annotation format and keep suppression separate from approval.
Set a review schedule that matches the volume and risk of requests. The MISRA lead, module owner, and safety or quality lead should assess the rationale, affected code, applicable permit conditions, and any needed tests or other safeguards.
Working With Generated and Adopted Code
Generated code, protocol stacks, and vendor drivers need an explicit compliance approach. Changing them may introduce risk or complicate future updates, but their origin is not a reason to ignore findings. Document what is checked, what evidence is available, and what limitations remain.
- Identify adopted and generated components and record their applicable treatment in the GRP and GEP.
- For generated code, retain the generator version, configuration, and analysis results for the output.
- Assess supplier evidence and deviations rather than assuming they satisfy the project's requirements.
- Review interfaces where component assumptions can affect code developed by the team.
- Record component versions and assess changes before accepting a new baseline.
A baseline update should preserve visibility of unresolved findings. It should not make violations disappear simply because a supplier or generator version changed.
Multi-Standard Reality Check
Embedded products may need to address MISRA alongside CERT C or C++ guidance, ISO/IEC TS 17961, or existing AUTOSAR C++14 requirements. Identify the actual contractual and product requirements before assuming that moving to a newer guideline set satisfies them.
One analysis workflow can support several standards when the checks and evidence are mapped carefully. Cross-references help avoid duplicate work, but a mapping does not prove that every requirement has been met.
Keep testing and other verification in the plan. A clean MISRA report does not demonstrate functional correctness, establish security, or provide functional-safety certification.
Code-Level Patterns That Reduce Triage Noise
Consistent coding practices can reduce recurring findings and make reviews easier. Two useful areas to address are memory allocation and controlling expressions.
Reduce Dynamic Allocation
Directive 4.12 and Rule 21.3 address dynamic memory allocation and standard library allocation functions in MISRA C:2023. Where practical, use statically allocated objects with clear ownership and lifetime.
If dynamic allocation remains necessary, centralizing it can make review and justification easier. A wrapper around an allocation function does not remove the underlying violation, and a statically sized pool does not automatically satisfy restrictions on dynamic allocation. Assess the actual behavior and document any required deviations.
Make Conditions Essentially Boolean
Rule 14.4 concerns controlling expressions with essentially Boolean type. For an integer count, an explicit test such as if (count != 0U) makes the condition clearer than if (count), provided the constant is appropriate for the type. For a pointer, if (ptr != NULL) makes the null check explicit.
Put these conventions in review guidance and automated checks. Explaining the intent helps developers avoid repeating the same pattern rather than merely fixing individual diagnostics.
Tooling Landscape: How to Evaluate
Evaluate tools against the GEP, not a generic coverage percentage. Ask for the guideline mapping for the chosen edition, supported compiler extensions, analysis limitations, and available report formats. Check how the tool distinguishes violations, false positives, and approved deviations.
Run a pilot on representative code, including shared headers, generated components, and hardware-specific constructs. Measure analysis time, review effort, and whether findings can be traced to the relevant build. Treat vendor coverage figures as claims to assess, not independent proof of compliance.
A Practical Rollout Plan
Sequence the work so policy, automation, and review develop together. The following schedule is an example, not a deadline for achieving compliance:
- First 30 days: confirm the target editions, assign responsibilities, agree on the GRP, and take a baseline scan.
- Days 31 to 60: complete the GEP, record tool and compiler configurations, enable new-code gates, and begin regular triage and deviation reviews.
- Days 61 to 90: add scheduled full-project analysis, publish evidence with builds, assess permits for recurring patterns, and work through legacy findings by risk.
Before a release claim, assess the entire agreed scope, including unresolved findings, manual checks, deviations, and adopted code. The rollout schedule should not override those acceptance criteria.
Compliance Is a System, Not a Scan
Credible MISRA compliance depends on policy, repeatable analysis, and human review working together. Tools identify potential problems, reviewers assess context and coverage gaps, and the records explain how the team reached its conclusions.
Agree on the documents early, prevent new violations, and keep remaining work visible. When evidence is maintained alongside the code, an audit becomes a review of ongoing engineering decisions rather than a last-minute reconstruction.