Connect with us
What Financial Institutions Actually Need from Enterprise Communication Software
Most engineering teams who move into financial services arrive with a reasonable assumption: this will be normal software work with more paperwork. Same languages, same patterns, same delivery rhythm, plus some compliance forms at the end.
That assumption survives about three weeks.
Banking software development is not ordinary development with regulation bolted on. The regulation changes the shape of the work itself, what you build, in what order, how you prove it, and what "done" means. Teams who understand that early ship. Teams who discover it late spend a year rebuilding foundations while their launch date slides.
Here is what actually changes when your users are banks, insurers, or anyone else operating under financial regulation
Compliance is an architecture decision, not a checklist
The most expensive misunderstanding in financial software development is treating compliance as a phase. Build the product, then make it compliant.
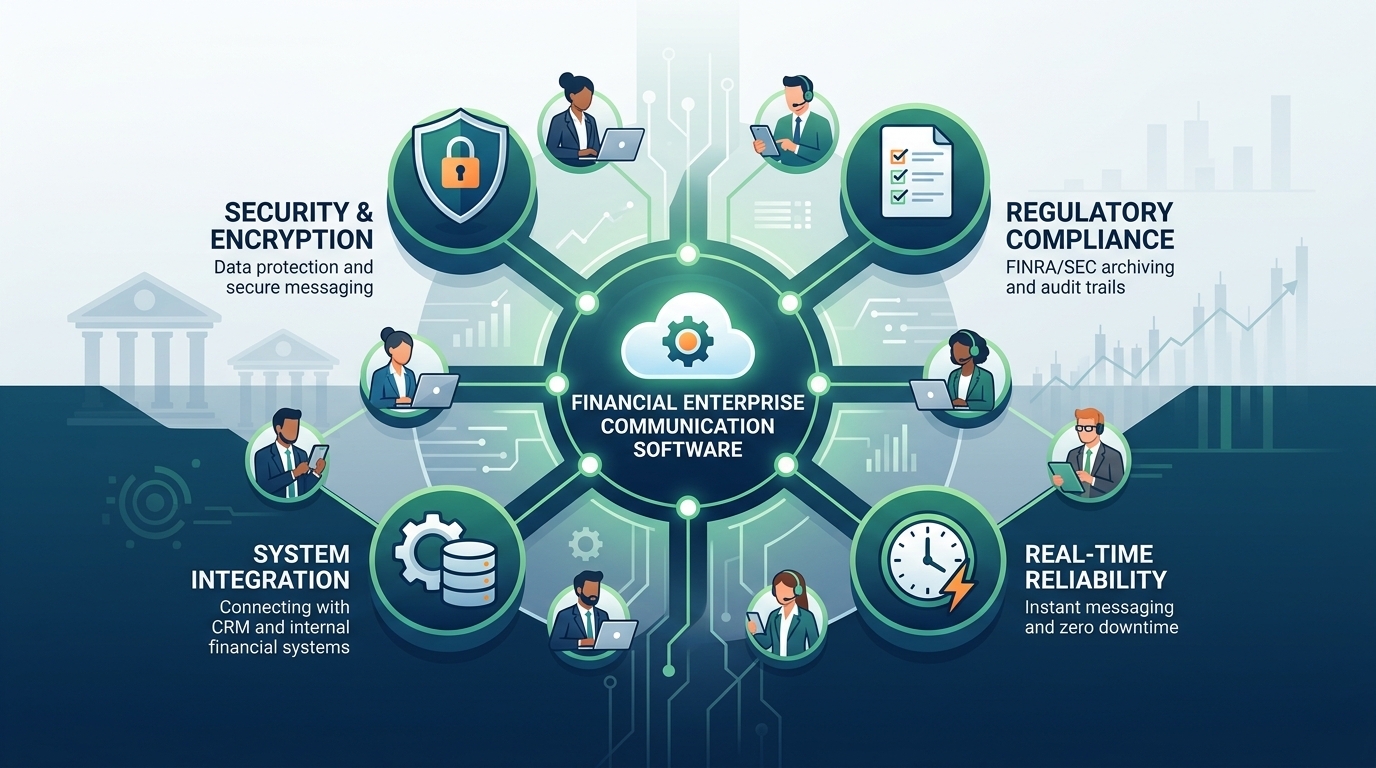
It does not work that way, because most regulatory requirements are structural. Data residency dictates where your infrastructure lives. Audit requirements dictate what every component logs and how immutably. Access controls dictate how identity flows through the entire system. Retention rules dictate your data model. None of these can be layered on top of a finished architecture, they are the architecture.
The practical consequence: on a regulated build, the compliance conversation has to happen at design time, with engineers in the room, not at the end with a legal review. Teams that defer it end up discovering that a core assumption, where data sits, how a service authenticates, what gets logged, is non-compliant at a depth that requires rewriting rather than patching.
You are not building for users, you are building for auditors too
In consumer software, the user is the audience. In software for banks, there is a second audience that never touches the interface: the auditor, the regulator, the risk committee.
That second audience does not care how elegant the product is. They care whether you can prove, after the fact, who did what, when, with what permissions, and that the record cannot have been altered. Which means audit logging is not a feature you add if there is time. It is a first-class part of the system, designed to be complete and tamper-evident from day one.
This reframes a lot of engineering decisions. A performance optimization that drops detail from logs is not a clean win, it may be a compliance regression. A convenient admin override that lets support staff fix a customer's record becomes a serious question about access control and traceability. In regulated environments, convenience features are where audit problems are born.
The integration surface is older and harder than you expect
Financial institutions run on systems that predate most of the people building against them. Core banking platforms, payment rails, settlement systems, and reporting infrastructure are frequently decades old, deeply reliable, and completely uninterested in your modern conventions.
Core banking integration in particular has a way of consuming timelines. Documentation may be thin. Sandbox environments may behave differently from production. Batch windows and settlement cycles impose timing constraints that a real-time-first team never considered. And the institution's own change-control process means every modification on their side moves at a pace you do not control.
The planning lesson is simple and widely ignored: do one real integration end to end before committing to a full delivery schedule. It will teach you more about your timeline than any estimate, and it surfaces the constraints that quietly reshape everything downstream.
Failure handling is the product
In most software, the happy path is the product and error handling is hygiene. In financial systems, the inverse is closer to true.
Money movement introduces states that have no equivalent in ordinary applications. A payment that partially completed. A transfer where the debit succeeded and the credit is unconfirmed. A duplicate request from a client that retried. A reconciliation mismatch between your ledger and a partner's. Every one of these needs a defined, correct, provable resolution, because the alternative is real money in an ambiguous state.
This is why idempotency, reconciliation, and immutable ledgers come up constantly in financial software and rarely elsewhere. It is also why regulated builds carry a testing burden that surprises teams: you are not just testing that the system works, you are testing that it behaves correctly when things go wrong, under conditions you have to deliberately manufacture.
Security is assumed, and proving it is the work
Every team says security matters. In regulated finance, saying it is not the job. Demonstrating it is.
Expect security questionnaires from partner institutions, penetration testing, and formal assessments before anything goes live. Expect to document your controls, your incident response, your key management, and your vendor chain. Expect that a bank's procurement process will scrutinize your secure software development practices in more depth than your product features.
The engineering implication is that security work has to be visible and documented as it happens, not reconstructed under pressure when a due-diligence request lands. Teams that treat documentation as an afterthought pay for it twice, once in the scramble, and again in the launch delay.
Build in-house or bring in experience
There is a real decision here, and it turns mostly on whether your team has done this before.
Keeping it in-house makes sense when financial engineering is your long-term advantage and you can actually hire people who have shipped regulated systems. The knowledge compounds and stays with you. The obstacle is that engineers who understand both modern software and the realities of compliance, settlement, and audit are genuinely scarce, and a team learning these lessons on your timeline is an expensive way to acquire them.
This is why a lot of institutions bring in a fintech software development company, firms like 10Pearls that have already been through the core integrations, the compliance architecture, and the partner due diligence elsewhere. You are buying experience of the failure modes rather than discovering them. The tradeoff is that some knowledge sits outside your organization, so if you go that route, be deliberate about what your own team owns and learns as you go.
The worst version is the accidental middle: generalist developers learning regulated finance on the job, with a delivery date set as though they already knew it.
The mindset that separates teams that ship
The teams who succeed in this space share one trait. They treat constraints as design inputs rather than obstacles.
They ask what has to be provable before they ask what would be elegant. They design the audit trail alongside the feature. They scope narrowly, one product, one market, one integration, because every addition multiplies the compliance surface rather than adding to it. And they build the failure paths first, because in financial software the failure paths are where trust is won or lost.
None of this makes the work slower in the end. It makes it slower at the start and dramatically faster afterward, which is the opposite of how most software projects are planned. That inversion is the whole lesson, and it is the one thing worth internalizing before writing a line of code for a bank.