Connect with us
CMMC and Your Collaboration Tools: What Defense Suppliers Must Lock Down First
Understanding the Importance of CMMC Compliance for Defense Suppliers
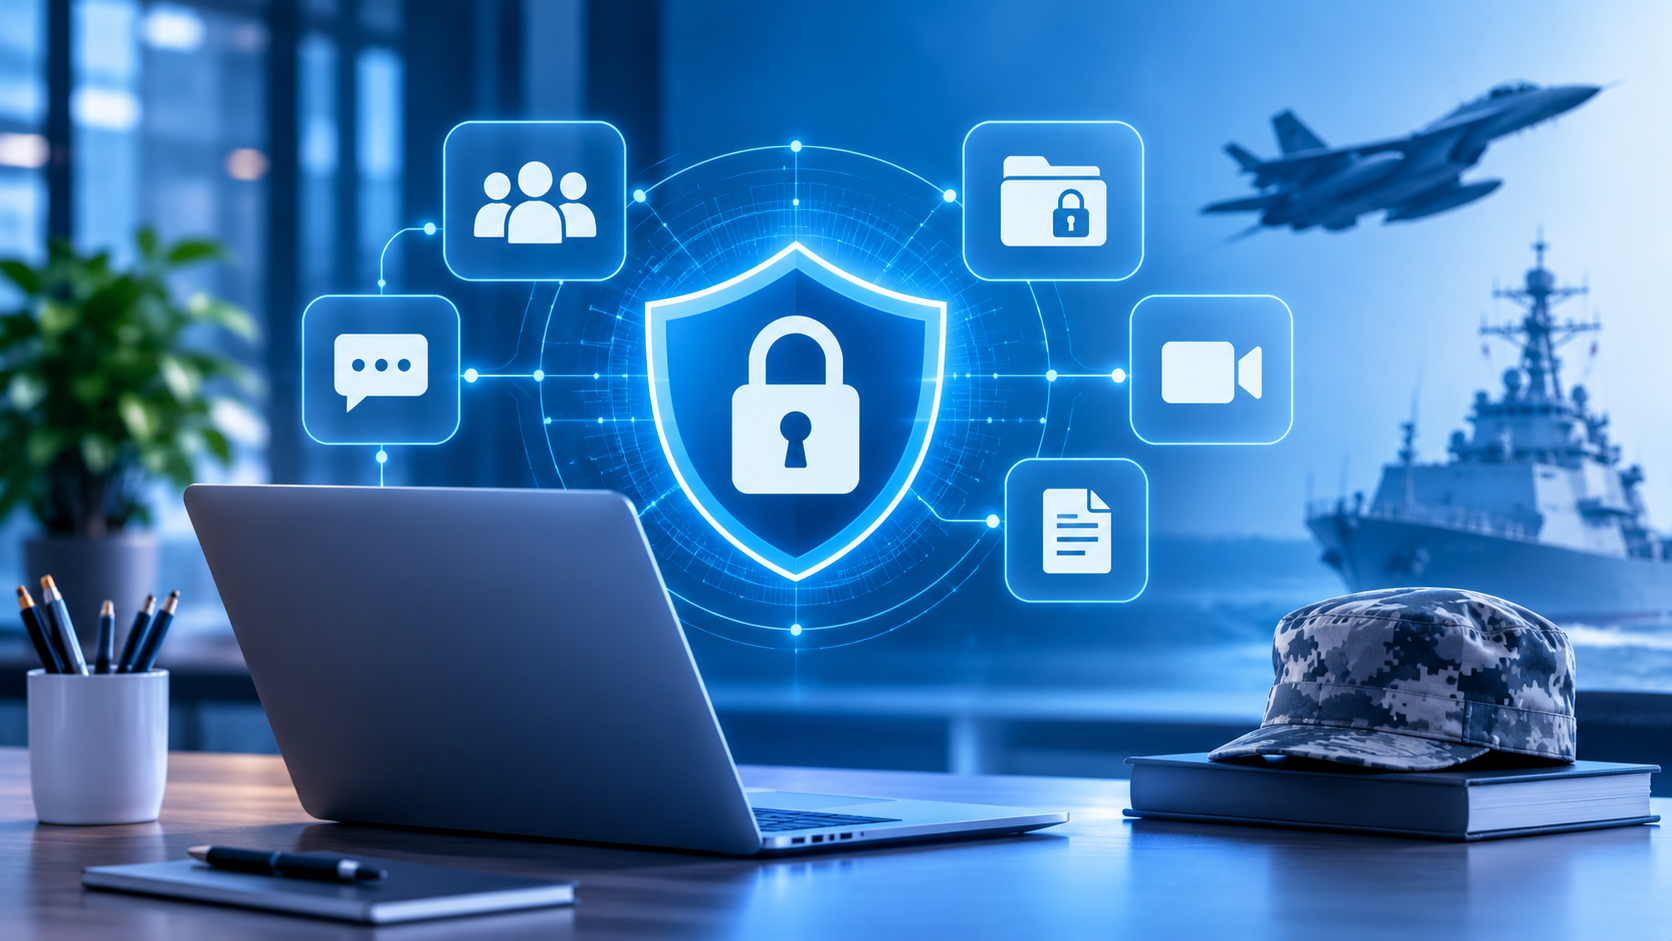
In the rapidly evolving landscape of defense contracting, cybersecurity has become a critical priority. The Cybersecurity Maturity Model Certification (CMMC) framework ensures that defense suppliers meet stringent cybersecurity standards before securing contracts with the Department of Defense (DoD). As cyber threats grow increasingly sophisticated, particularly those targeting sensitive government data, defense suppliers must focus on securing their collaboration tools. These tools, which facilitate communication and data sharing across organizations, are often the first vectors exploited by cyber adversaries.
Collaboration tools-from messaging platforms and video conferencing apps to file-sharing and project management software-are integral to daily operations for defense suppliers. However, their widespread adoption also makes them prime targets for cyberattacks. According to a recent report, approximately 68% of breaches within defense supply chains originate from vulnerabilities in communication and collaboration systems. This underscores the urgent need for defense suppliers to ensure these tools comply with rigorous cybersecurity standards and are fortified against exploitation.
In this article, we explore how defense suppliers can align their collaboration tools with CMMC requirements, what features to prioritize, and practical steps to improve security posture-all while maintaining operational efficiency.
The Foundation: Protek’s Cybersecurity Standards
Before delving into collaboration tool security specifics, it’s important to understand the foundational guidelines underpinning CMMC compliance. Protek's cybersecurity standards provide a comprehensive set of cybersecurity standards that align closely with CMMC objectives. These standards emphasize a holistic approach, combining technical controls with organizational policies to defend against cyber threats effectively.
Protek’s approach focuses on securing data in transit and at rest, enforcing strict access controls, and implementing continuous monitoring. These measures are especially relevant for collaboration environments, where sensitive data frequently moves between users and systems. Adopting these standards helps defense suppliers reduce risks such as unauthorized access, data leakage, and insider threats-challenges historically plaguing the defense sector.
For example, encryption protocols recommended by Protek ensure that data shared via collaboration tools remains confidential and tamper-proof during transmission and storage. Continuous monitoring detects unusual activity in real time, enabling rapid response to potential breaches before significant damage occurs.
Collaboration Tools: The First Line of Defense
Collaboration platforms are more than communication channels-they often serve as repositories for sensitive data, including controlled unclassified information (CUI), which must be protected under CMMC. Suppliers must ensure their collaboration tools incorporate strong security features such as encryption, multi-factor authentication (MFA), and detailed audit logging.
The importance of MFA cannot be overstated. A study by the Ponemon Institute found that organizations implementing MFA saw a 99.9% reduction in account compromise attacks (source: https://www.ponemon.org/blog/multi-factor-authentication-the-best-defense-against-cyberattacks). This demonstrates MFA is not just a compliance checkbox but a critical control that drastically lowers the risk of unauthorized access through compromised credentials.
Additionally, audit logs enable organizations to track user activities and identify suspicious behavior, essential for timely incident response and forensic investigations. Encryption protects data integrity and confidentiality, ensuring that even if intercepted, information remains unreadable to attackers.
Given the sensitive nature of defense contracts, collaboration tools must also support role-based access controls (RBAC) to limit users’ permissions strictly to information necessary for their roles. This minimizes the attack surface and helps prevent insider threats or accidental data exposure.
Insights from Industry Experts
Navigating CMMC compliance complexities can overwhelm defense suppliers, especially when balancing cybersecurity needs with operational demands and budget constraints. insights by Cyber Security Solutions offer valuable insights into optimizing cybersecurity investments, highlighting common pitfalls and best practices for securing collaboration tools.
Many defense suppliers underestimate hidden costs of securing collaboration environments, including software licensing fees, employee training, and ongoing maintenance. Experts emphasize budgeting for these elements upfront is critical to avoid security gaps and costly remediation efforts later.
Moreover, integrating cybersecurity considerations into procurement and operational workflows is essential. Rather than viewing security as an afterthought, organizations should embed it into every phase of tool selection, deployment, and use. This proactive approach ensures compliance and fosters a culture where cybersecurity is a shared responsibility.
Industry experts also recommend leveraging automation and artificial intelligence to enhance continuous monitoring and threat detection. These technologies help identify anomalies faster and reduce the burden on security teams.
Key Features to Lock Down in Collaboration Tools
To comply with CMMC requirements effectively, defense suppliers should prioritize securing these features within their collaboration platforms:
- Data Encryption: Employ strong encryption algorithms to protect data at rest and in transit. This ensures sensitive information like CUI remains confidential and secure from interception or unauthorized access.
- Access Controls: Implement role-based access controls (RBAC) to restrict user permissions based on job functions, minimizing accidental or malicious data exposure.
- Multi-Factor Authentication (MFA): Require MFA for all user logins to add a layer of protection beyond passwords, drastically reducing account compromise risks.
- Audit Trails and Logging: Maintain detailed logs of user activities, including file access, sharing, and modifications, supporting incident investigation and accountability.
- Regular Software Updates and Patch Management: Keep collaboration tools up to date with the latest security patches to address known vulnerabilities and defend against emerging threats.
- Data Loss Prevention (DLP) Capabilities: Incorporate DLP features to monitor and control sensitive data movement within collaboration platforms, preventing accidental leaks.
- Secure Configuration and Hardening: Follow best practices for configuring collaboration tools securely, disabling unnecessary features and services that could introduce vulnerabilities.
Integrating CMMC Compliance into Daily Operations
Technical controls alone are insufficient without fostering a culture of security awareness among employees. Defense suppliers must invest in comprehensive training tailored to risks posed by collaboration tools. Human error remains a leading cause of data breaches, making education critical.
Training should cover recognizing phishing attempts, securely sharing files, using MFA, and reporting suspicious activity. Regular refresher courses reinforce good security hygiene and keep employees informed about evolving threats.
In addition to training, continuous monitoring and regular audits maintain compliance and identify improvement areas. Cyber threats evolve rapidly, and defenses must adapt. Automated monitoring tools alert security teams to anomalous behaviors, such as unusual login locations or data transfers, enabling swift investigation.
Periodic audits-internal and external-verify security policies and controls are effective and aligned with CMMC guidelines. These audits prepare organizations for formal CMMC assessments required to maintain certification.
The Business Impact of Secure Collaboration
Securing collaboration tools delivers benefits beyond regulatory compliance. A robust cybersecurity posture enhances trust with DoD partners and other stakeholders, positioning defense suppliers as reliable partners in national security.
The financial implications of poor cybersecurity are significant. IBM estimates the average cost of a data breach in the defense sector at $4.24 million. This includes incident response and remediation costs plus reputational damage and lost business opportunities.
Conversely, investing in secure collaboration environments improves operational efficiency by streamlining workflows and reducing disruption risks from cyber incidents. Secure tools enable teams to collaborate confidently, knowing sensitive information is protected at every stage.
Furthermore, maintaining CMMC compliance is increasingly a prerequisite for winning and retaining defense contracts. Suppliers who fail to meet these standards risk losing business and facing legal and financial penalties.
Moving Forward: Practical Steps for Defense Suppliers
To align collaboration tools with CMMC requirements and strengthen cybersecurity posture, defense suppliers should consider these actionable steps:
- Conduct a Comprehensive Risk Assessment: Identify vulnerabilities and risks specific to collaboration tools, including potential attack vectors and data exposure points.
- Engage Cybersecurity Experts: Collaborate with specialized professionals to design, implement, and validate security controls tailored to organizational needs.
- Update Policies and Procedures: Ensure security policies reflect current CMMC guidelines and incorporate best practices for secure collaboration.
- Invest in Employee Training: Develop ongoing programs focused on secure use of collaboration tools and cyber threat awareness.
- Implement Continuous Monitoring and Auditing: Utilize automated tools to detect anomalies and conduct regular audits verifying compliance and identifying gaps.
- Regularly Review and Upgrade Technologies: Stay current with emerging security technologies and update collaboration platforms to address new vulnerabilities.
- Plan for Incident Response: Establish clear procedures for responding to security incidents involving collaboration tools, including communication protocols and remediation steps.
Conclusion
As the defense supply chain faces mounting cybersecurity challenges, securing collaboration tools is critical to maintaining CMMC compliance and protecting sensitive information. These tools, fundamental to daily operations, must be fortified with encryption, access controls, MFA, and continuous monitoring to withstand evolving cyber threats.
By leveraging established cybersecurity standards such as those provided by Protek, incorporating expert insights to optimize investments, and embedding security awareness into organizational culture, defense suppliers can confidently meet CMMC requirements. Doing so safeguards operations and enhances trust and competitiveness within the defense industry.
Locking down collaboration tools is not merely a regulatory obligation—it is a strategic imperative that protects national security interests and supports the integrity of the defense supply chain.